


68 Software Firms Sign CISA’s Secure-by-Design Pledge
A year since CISA’s initiative, tech companies say their products will have built-in security features from the start.
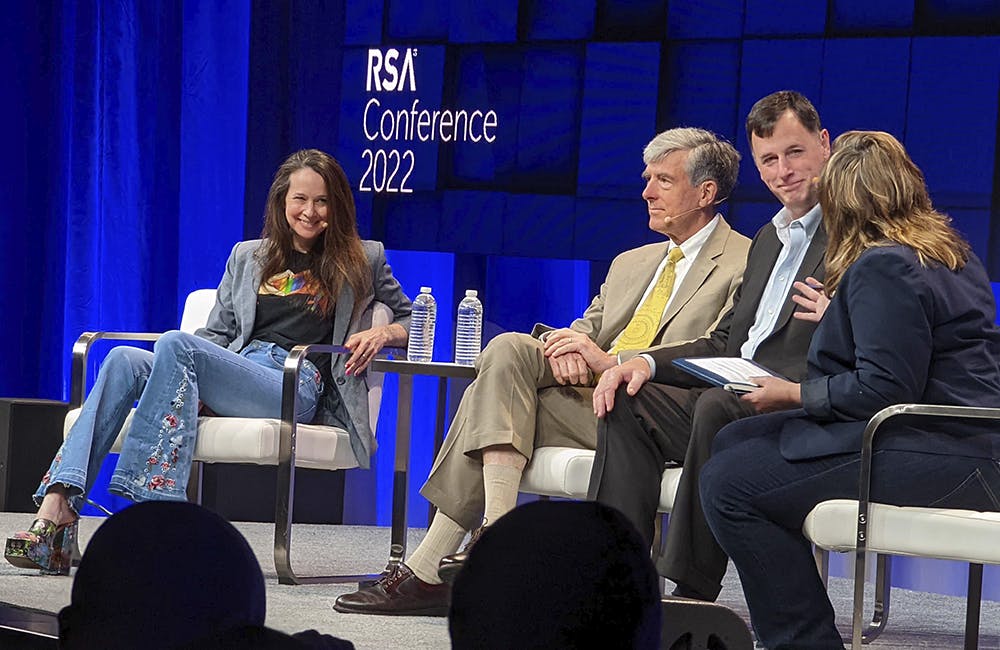
The Cybersecurity Infrastructure and Security Agency (CISA) this week said 68 software manufacturers, including big-tech giants like Microsoft and Google, voluntarily joined CISA’s Secure by Design pledge that aims to design technology with default security features, rather than security being an afterthought.
“More secure software is our best hope to protect against the seemingly never-ending scourge of cyberattacks facing our nation. I am glad to see leading software manufacturers recognize this by joining us at CISA to build a future that is more secure by design,” CISA Director Jen Easterly said in a press release. “I applaud the companies who have already signed our pledge for their leadership and call on all software manufacturers to take the pledge and join us in creating a world where technology is safe and secure right out of the box.”
Earlier this year, Easterly called on agencies to practice cyber hygiene and cited the secure-by-design framework. The pledge contains seven goals based on using multi-factor authentication, eliminating default passwords, reducing classes of vulnerabilities, increasing security patches, public disclosure of vulnerabilities, increasing transparency of vulnerabilities by reporting promptly and taking ownership of customers’ security outcomes. The companies that signed the pledge have one year to show progress.
While the pledge is focused on software products and services, like on-premise software, cloud services and software as a service, CISA encourages manufacturers of physical products to document their progress as well.
“Every software manufacturer should recognize that they have a responsibility to protect their customers, contributing to our national and economic security. I appreciate the leadership of those who signed on and hope that every technology manufacturer will follow suit,” said CISA Senior Technical Advisor Jack Cable.
To date, the following 68 companies have signed the pledge: 1touch.io, Akamai, Amazon Web Services, Apiiro, Armis, Automox, BigID, BlackBerry, Bugcrowd, Chainguard, Cisco, Claroty, Cloudflare, CrowdStrike, Cybeats, Resilience, ESET, Everfox, Finite State, Forescout, Fortinet, Gigamon, GitHub, GitLab, Google, Hewlett Packard Enterprise, HiddenLayer, HP, Huntress, IBM, Infoblox, InfoSec Global, Ivanti, Kiteworks, Lasso Security, Lenovo, Manifest, Microsoft, N-able, NetApp, Netgear, Okta, Palo Alto Networks, Pangea, Proofpoint, Qualys, Rapid7, Red Queen Dynamics, Scale AI, Secureworks, Securin, Security Compass, SentinelOne, Socket, Sonatype, Sophos, Tenable, ThreatQuotient, ThriveDX, Tidelift, Trellix, Trend Micro, Vanta, Veracode, Veritas Technologies LLC, Wiz, Xylem and Zscaler.

This is a carousel with manually rotating slides. Use Next and Previous buttons to navigate or jump to a slide with the slide dots
-

IT Officials Are Finding Efficiencies Across Cloud, Data Networks
Federal government agencies are utilizing data to integrate capabilities into environments and better deliver on mission.
4m read -

Agencies Seek Faster Cloud Adoption, Control Over IT Costs
New tools, faster contracting and automated compliance are helping agencies address challenges in modernizing legacy systems.
2m read -

The Cybersecurity Nightmares Threatening Modern Organizations
Cybersecurity leaders examine the hidden threats facing organizations, from shadow AI and legacy systems to alert fatigue, analyst burnout and emerging AI risks.
17m watch -

Army's Project Gatekeeper Platform to Launch This Month
Acting Army CIO Gabe Chiulli said the service’s new DevSecOps platform designed to more efficiently engage industry will debut on Oct. 23.
3m read


