


Application Security is a Core Tenet of Zero Trust
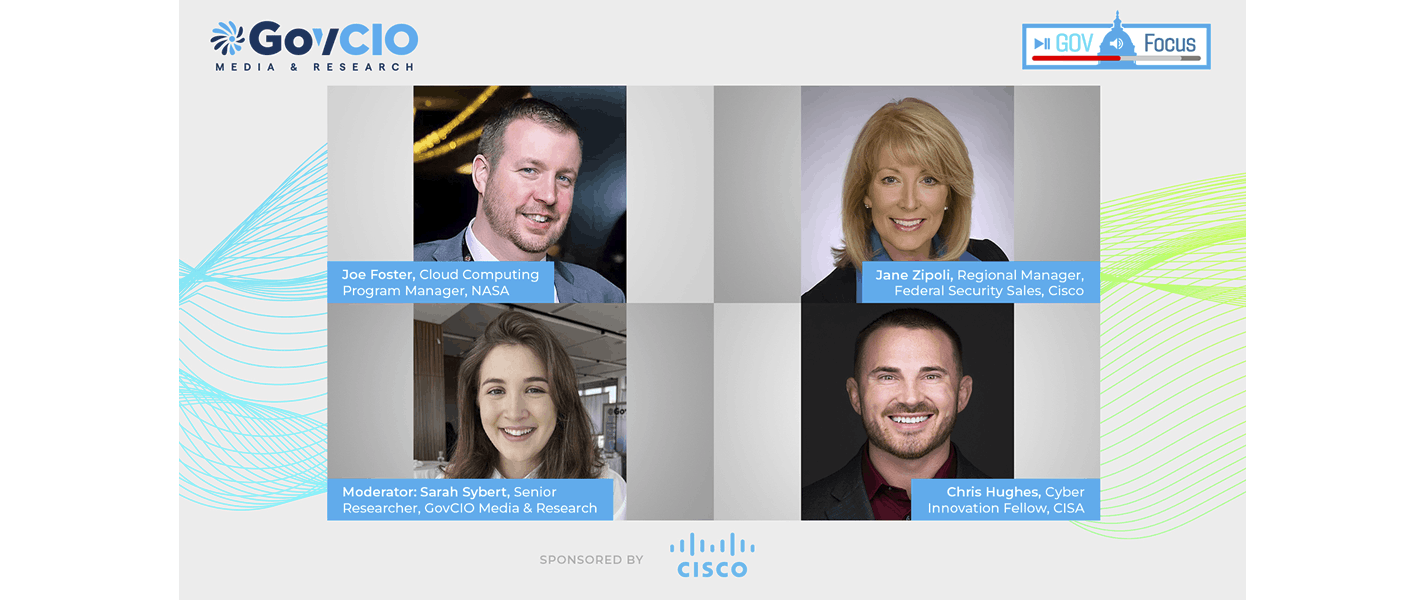
Zero trust requires all users to be authenticated, authorized and continuously validated for security posture before accessing applications and data. As organizations make progress in their zero trust journeys, leaders are focusing on the next challenge: software application security. These leaders dive into the strategy, testing and evaluation, advances in analytics and more that are bolstering security features within applications to prevent vulnerabilities against evolving threats.
-
 Joe Foster Cloud Computing Program Manager, NASA
-
 Chris Hughes Cyber Innovation Fellow, CISA & Co-Founder and CISO, Aquia
-
 Jane Zipoli Regional Manager, Federal Security Sales, Cisco


-

New CDM Security Service Aims to Cut Cyber Response Times
CISA’s SIEM-as-a-Service platform gives federal agencies automated tools to improve threat hunting, logging and incident response.
3m read -

Treasury Expands Do Not Pay System to Prevent Improper Payments
Treasury expects 70% to 80% of government programs to fully use Do Not Pay as it expands tools to prevent improper payments.
3m read -

How Agencies are Moving from AI Pilots to Mission-Ready Workflows
Officials explore the data foundations, experimentation strategies and security safeguards needed to put AI into practice.
41m watch Partner Content -

Inside ASPR’s Efforts to Bolster Healthcare Sector Cyber Resilience
HHS ASPR’s Bob Bastani details how governance, standards and migration planning can help against emerging threats to medical data and devices.
12m watch


