


Officials: HHS Cyber Attack Shows Importance of Cybersecurity Amid Pandemic Response
While the attack was reportedly unsuccessful, federal cybersecurity leads encourage agencies to ‘remain vigilant’.
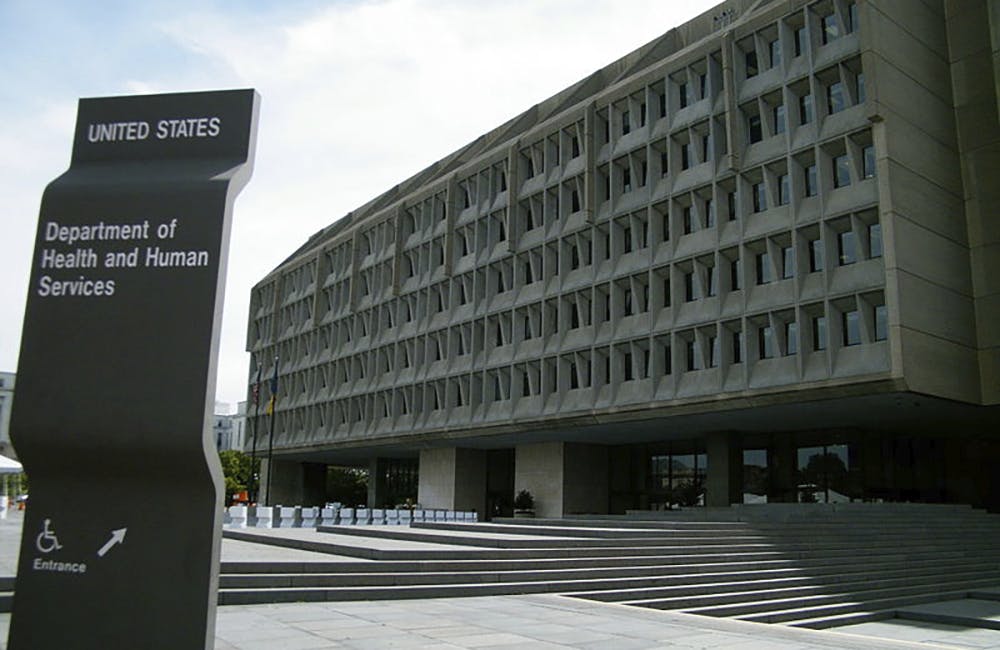
The recently reported cyberattack on the Department of Health and Human Services Sunday underscores the importance of securing the digital infrastructure of the federal agencies responding to the coronavirus pandemic, security officials said.
HHS cybersecurity teams noticed increase scanning activity on the agency’s systems Sunday evening, consistent with the early stages of a distributed denial of service (DDoS) incident, according to published reports. DDoS attacks overload systems with requests, slowing down or effectively disabling those systems, but in this instance, it appears the attack was unsuccessful.
“Text message rumors of a national #quarantine are FAKE,” the National Security Council tweeted at about the same time the incident occurred. “There is no national lockdown. @CDCgov has and will continue to post the latest guidance on #COVID19. #coronavirus”
It is unclear if this tweet was in response to the attempted DDoS attack or a coincidental message to counter disinformation. At this time, no data or information appears to have been stolen during the incident.
Federal law enforcement cyber response teams, including those at FBI and the Department of Homeland Security, are analyzing the incident and working to identify the actors behind it.
“HHS has an IT infrastructure with risk-based security controls continuously monitored in order to detect and address cybersecurity threats and vulnerabilities,” said HHS Spokesperson Caitlin Oakley. “On Sunday, we became aware of a significant increase in activity on HHS cyber infrastructure and are fully operational as we actively investigate the matter. Early on while preparing and responding to COVID-19, HHS put extra protections in place. We are coordinating with federal law enforcement and remain vigilant and focused on ensuring the integrity of our IT infrastructure.”
Recognizing that attacks on healthcare organizations can lead to life-or-death situations, HHS has information sharing networks in place, HHS Chief Information Security Officer Janet Vogel and Deputy CISO Chris Bollerer explained on CyberCast.
Through the Health Sector Cybersecurity Coordination Center, HHS communicates with healthcare providers around the nation on both emerging threats and defensive actions. Vogel added that HHS also communicates with the Veterans Health Administration and Defense Health Agency to secure patient data, medical devices and other systems across federal healthcare.
The Cybersecurity and Infrastructure Security Agency encourages both public and private organizations to remain vigilant, especially for phishing attempts related to COVID-19.
“The Cybersecurity and Infrastructure Security Agency warns individuals to remain vigilant for scams related to Coronavirus Disease 2019 (COVID-19),” the agency said in an official release. “Cyber actors may send emails with malicious attachments or links to fraudulent websites to trick victims into revealing sensitive information or donating to fraudulent charities or causes. Exercise caution in handling any email with a COVID-19-related subject line, attachment, or hyperlink, and be wary of social media pleas, texts, or calls related to COVID-19.”
Lawmakers recognize the potential for these attacks during uncertain times and the necessity for a strong response.
“Here’s the reality of 21st century conflict: cyberattacks are massive weapons to kick opponents when they’re down,” said U.S. Sen. Ben Sasse, R-NE, in a public statement. “At a time when Americans face uncertainty and fear from coronavirus, we should expect an increase in cyberattacks and stay vigilant. There need to be consequences for these kinds of attacks. We can’t take our eye off the ball.”


This is a carousel with manually rotating slides. Use Next and Previous buttons to navigate or jump to a slide with the slide dots
-

PHP Warning Highlights Battle Between AI Speed, Cyber Hygiene
CISA warned organizations to patch a pair of hypertext vulnerabilities that would allow intruders remote server access.
3m read -

NIST Developing Tailored Cybersecurity Controls for AI Systems
The COSIS project will include five volumes of standards for control overlays on a variety of AI and super intelligence systems.
3m read -

Preparing for PQC Migration at Federal Agencies
NIST, DOW and industry leaders discuss how agencies can prepare systems, prioritize risks and scale the transition to post-quantum cryptography.
27m watch Partner Content -

How CDM Is Evolving to Counter Emerging Cyber Threats
CISA’s Acting Associate Director for Capacity Building and CDM Program Director discusses how the program is now tackling threat mitigation.
31m watch


